For IT & data protection

Clear architecture. Clear responsibility.

Technical buyers don’t need marketing shortcuts, they need verifiable statements on data, access, integrations, AI actions and operations.

The questions we usually get from IT

Four questions that
come before signature.

We answer with diagrams, contract text and log examples, not marketing lines.

01

Where does the data live?

US cloud? Model training on your data? Which processing agreement?
02

How is AI traceable?

Log? Approval logic? Roles? Auditable also after 12 months?

03

What happens in an incident?

Instant kill-switch on all AI actions? Who gets notified?

04

What do we get if we switch away?

Data export in open formats, handover of integrations, documented processes.
Traceable
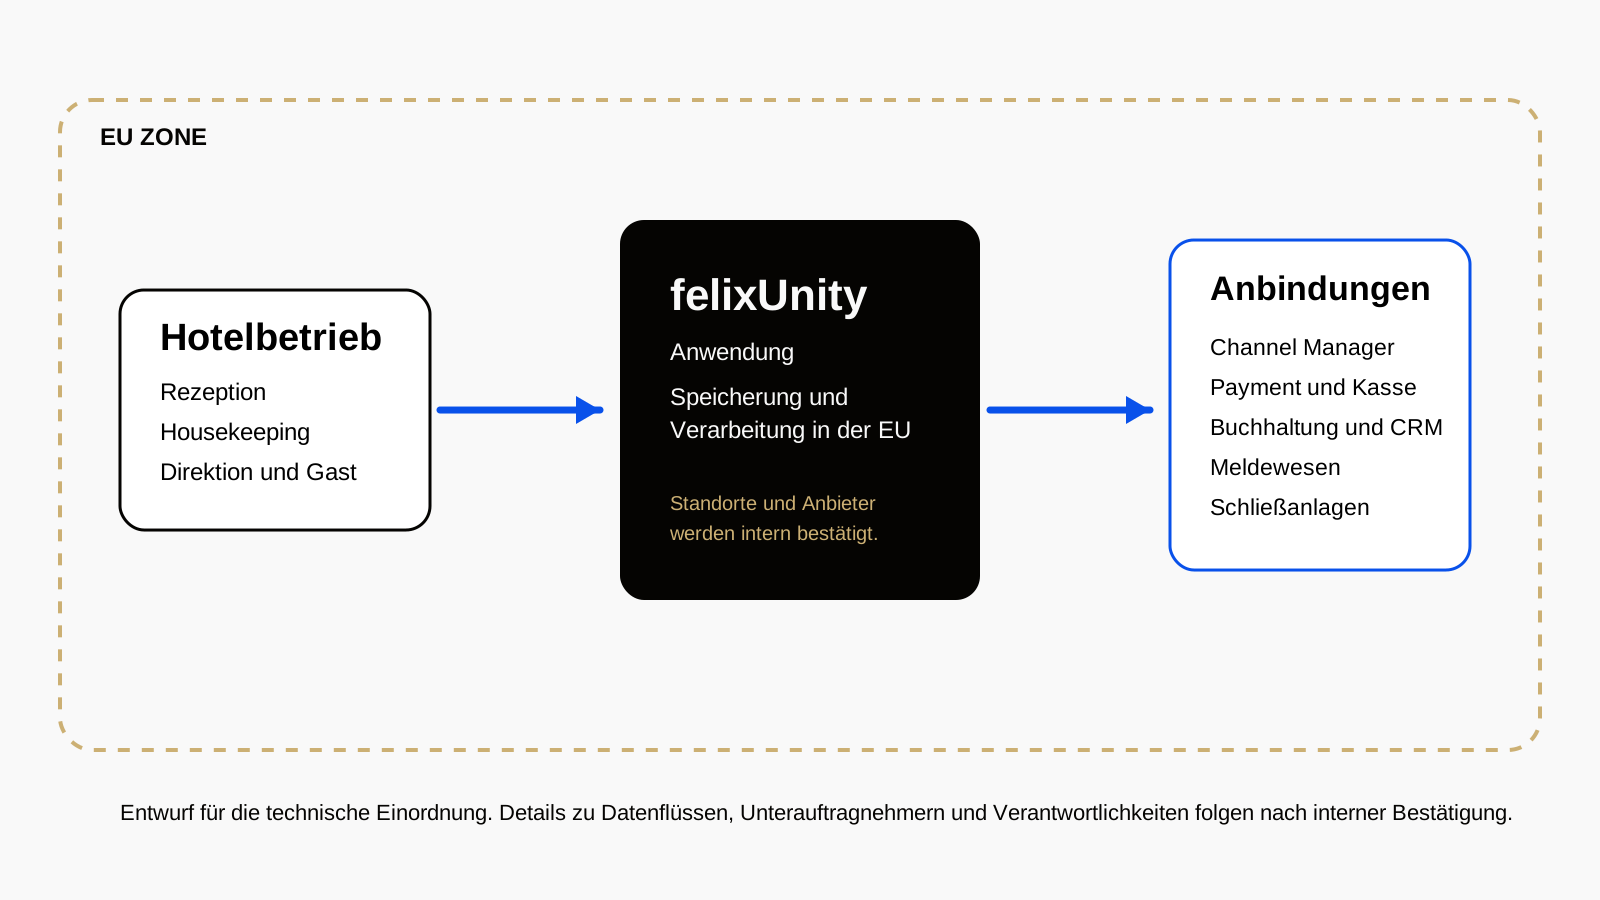
Overview of felixUnity's system architecture with connected systems
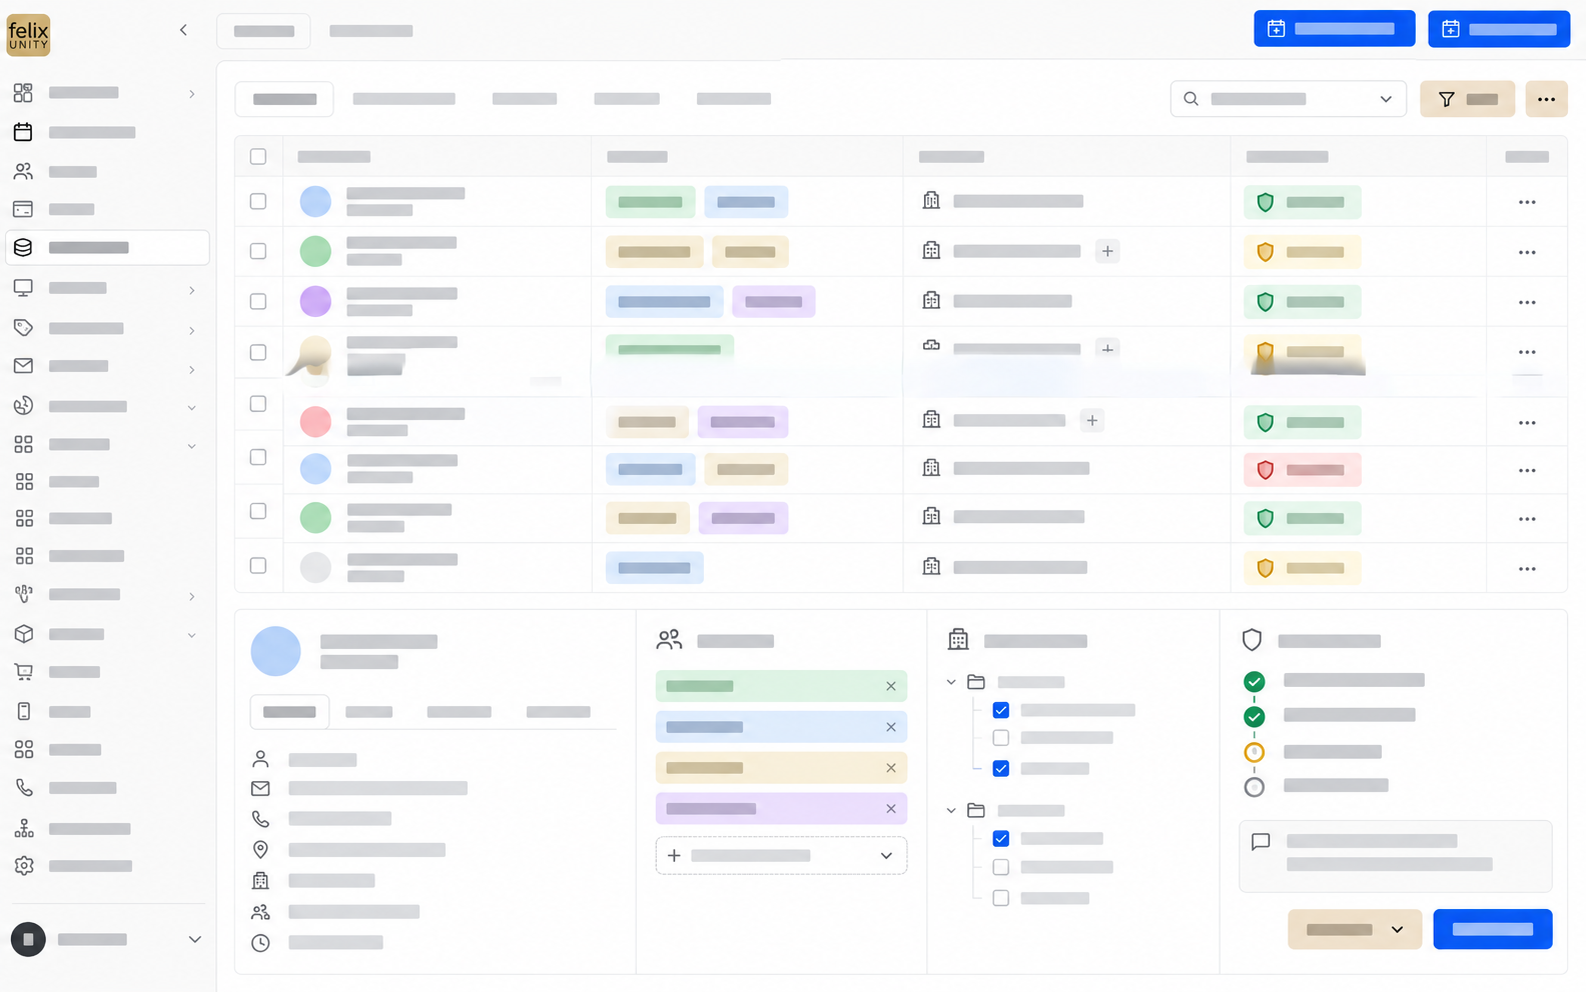
Anonymous roles and permissions view in felixUnity

Data & privacy

  • EU processing locations
  • DPA and sub-processors
  • Deletion and retention policy
  • No training on customer data

Identity & access

  • Role and permission model
  • Approvals for critical AI actions
  • Logging and traceability
  • SSO/MFA

Integration & data flow

  • API and partner documentation
  • Error and retry behaviour
  • Monitoring and ownership
  • Export and portability options

Operations & resilience

  • SLA, support and escalation
  • Backups, RTO and RPO
  • Incident and vulnerability process
  • Release and change management
Ready for the detail questions?

Let’s talk architecture,
data and responsibility.

We bring data-flow diagrams, processing agreement, role model and log examples, and answer your compliance points directly.

What we bring:

  • Data flows as diagrams, not a wall of text
  • Data processing agreement and GDPR evidence
  • Approval logic, roles and audit log live
Get in touch