For IT & data protection

Clear architecture. Clear responsibility.

Technical buyers do not need marketing shortcuts, but verifiable statements on data, access, integrations, AI actions and operations.

What your IT team typically asks

Four questions that come before
the signature.

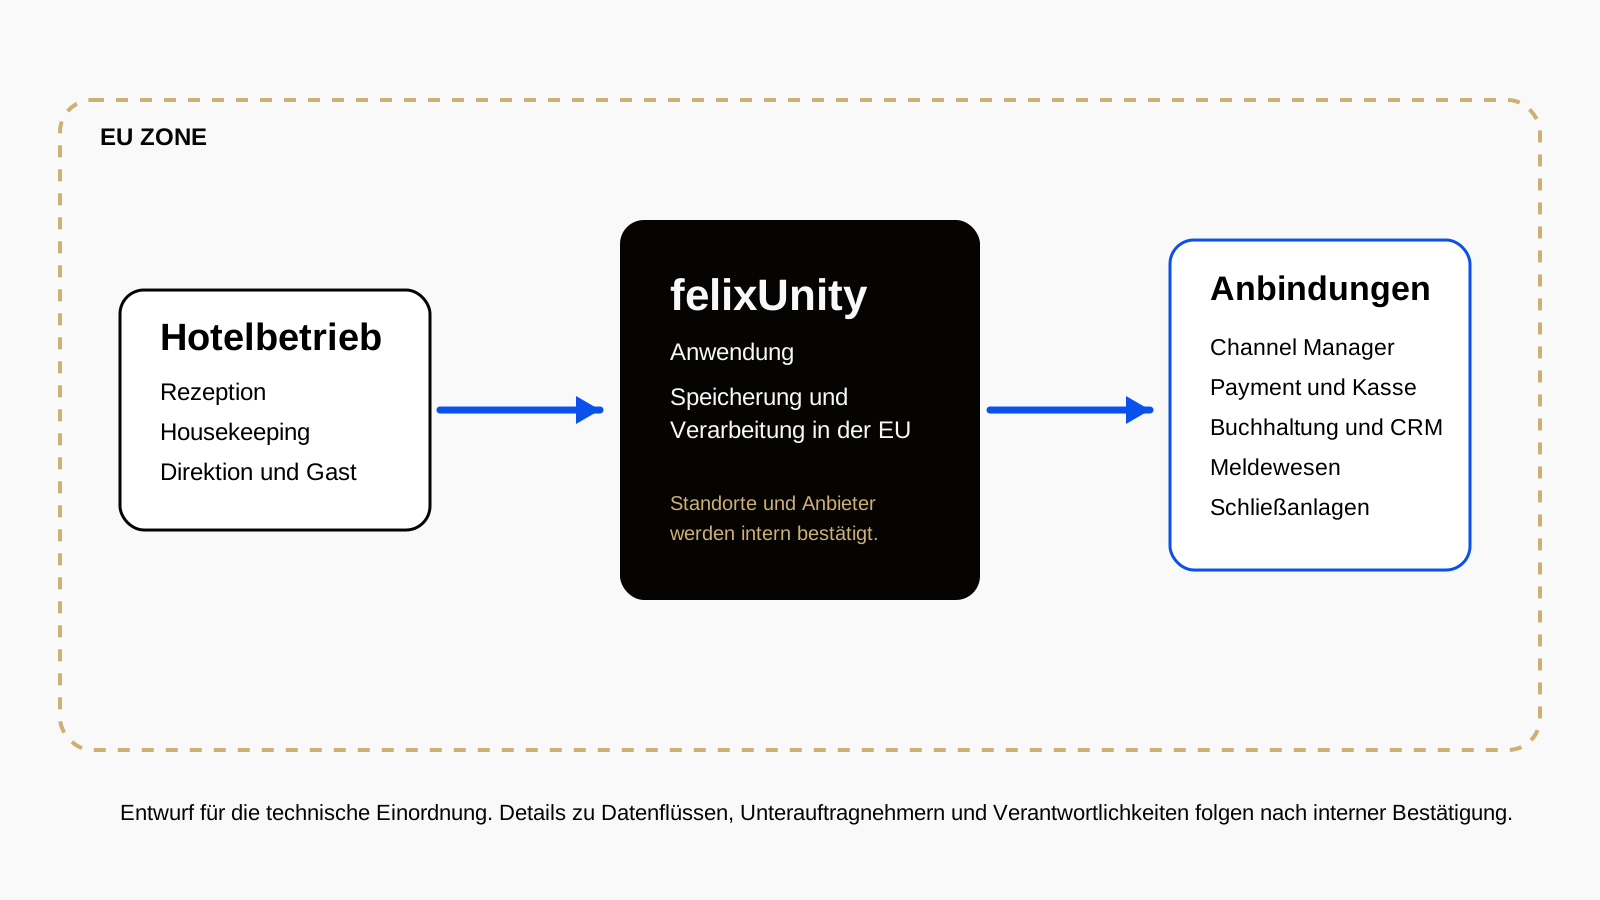
Instead of glossy answers, there are documents you can check: an architecture diagram, the data processing agreement, examples from the audit log and the role model. What we say can be verified.

01

Where is the data?

US cloud? Model training on your data? Which data processing agreement is included?
02

How is AI traceable?

Log? Approval logic? Roles? Auditable even after 12 months?

03

What happens in an incident?

Immediate kill switch for all AI actions? Who gets notified?

04

What do we get if we switch?

Data export in open formats, handover of the integrations, documented processes.
Traceable
Overview of the felixUnity system architecture with connected systems
Anonymized view of roles and permissions in felixUnity

Data & data protection

  • EU processing locations
  • DPA and sub-processors
  • Deletion and retention concept
  • No training on customer data

Identity & access

  • Role and permission concept
  • Approvals for critical AI actions
  • Logging and traceability
  • SSO/MFA

Integration & data flow

  • API and partner documentation
  • Error and retry behaviour
  • Monitoring and accountability
  • Export and portability options

Operations & resilience

  • SLA, support and escalation
  • Backups, RTO and RPO
  • Incident and vulnerability process
  • Release and change management
Ready for the detailed questions?

Let’s talk about architecture,
data and responsibility.

We bring data flow diagrams, the data processing agreement, role model and examples from the log, and answer your compliance points directly.

What we bring:

  • Data flows as a diagram, not a wall of text
  • Data processing agreement and GDPR evidence
  • Approval logic, roles and audit log, live
Get in touch